Remote Server Login
RDP · SSH · Jump hosts
Read moreReplace standing administrator rights with vaulted credentials, Just-In-Time elevation and a searchable recording of every privileged session.
Privileged, administrative and shared accounts are often unmanaged — with standing access, shared credentials and little session visibility. They are the accounts that turn a minor intrusion into a serious one.
The inventory problem comes first. Most organisations discover they have considerably more privileged, service and shared accounts than anyone believed, spread across systems that were each somebody's responsibility at some point.
| Before | After |
|---|---|
| Administrator passwords are known to several people. | Nobody needs to know the credential; the vault holds it. |
| Privilege is permanent once granted. | Privilege is temporary and expires without anyone remembering. |
| Nobody can prove what an administrator did. | Every session is recorded and searchable. |
Privileged, admin, service and shared accounts across the estate are found and inventoried.
Credentials move into an encrypted vault with automatic rotation, out of scripts and spreadsheets.
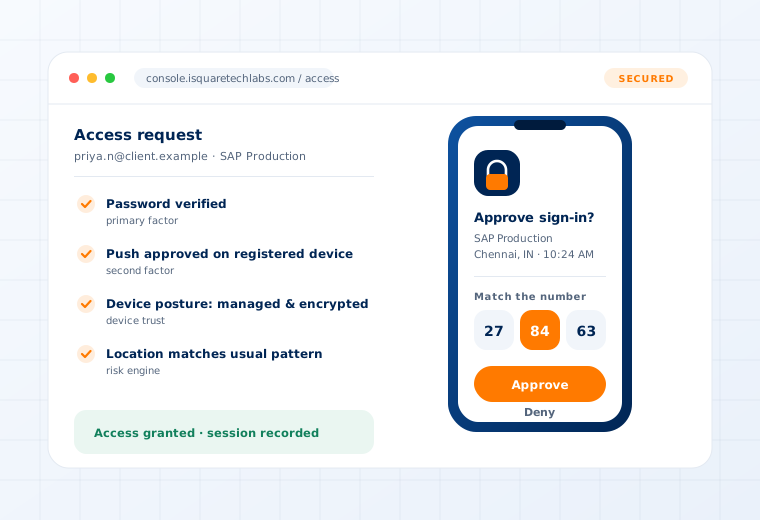
Access is granted just in time, for a defined window, against an approved reason.
Sessions are brokered and recorded, giving auditors a searchable trail of what was done.
If yours is not here, our team will answer it directly.
Ask usBring the system you are worried about and we will show you exactly how this control would be applied to it.