Vault
Secure privileged credentials in an encrypted enterprise vault, and discover privileged, admin, service and shared accounts across the estate.
One platform brings identity lifecycle, access management, multi-factor authentication, privileged access and governance together — replacing the identity silos that widen your attack surface.
Modern enterprises operate across a growing mix of cloud services, SaaS applications, on-premises systems, mobile devices, remote users and privileged accounts — with identity data scattered across many directories and platforms.
Privileged, administrative and shared accounts are often unmanaged — with standing access, shared credentials and little session visibility. This fragmented approach increases security risk, administrative complexity, compliance challenges and operational cost.
Modular by design. Subscribe to MFA, IAM or PAM on their own, or deploy the full platform.
Out-of-Band, risk-based MFA that defeats phishing, MITM and SIM-swap — protecting workforce access across apps, VPNs, desktops and remote environments.
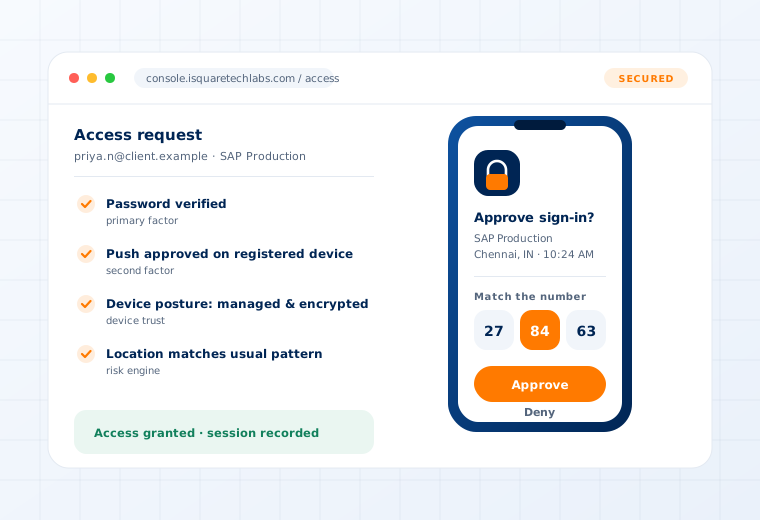
One secure front door to every application — with federation, SSO, identity brokering and adaptive, policy-based access controls.
Automate provisioning, deprovisioning and identity synchronisation across enterprise systems — integrated with Active Directory, LDAP, HR systems, applications and cloud.
Govern access with automated lifecycle management and turn identity data into actionable insight through centralised reporting and analytics.
Secure, monitor and audit privileged accounts with credential vaulting, Just-In-Time access and session recording — cutting insider and credential-theft risk.
Secure privileged credentials in an encrypted enterprise vault, and discover privileged, admin, service and shared accounts across the estate.
Enforce least-privilege and Just-In-Time access policies, so standing privilege is replaced by access that expires on its own.
Monitor, record and audit privileged sessions, reducing insider-threat and credential-theft risk with evidence your auditor can follow.
We will show adaptive MFA, SSO and PAM working on a system you already run — on-premise, private cloud or as a service.