Endpoint Agent
Runs on every device. Guards clipboard, USB, print, screenshot, file-save and image-open, with on-device OCR.
One cross-platform agent for Windows, Linux and macOS guards clipboard, USB, print, screenshot, files, web, email, AI tools and messengers — enforcing at the operating-system layer, before anything is encrypted.
Classic DLP watches the network wire. But data leaves through a dozen channels the network never sees — and the hardest one, end-to-end encrypted messengers, is opaque ciphertext by the time it hits the wire.
By the time encrypted upload traffic reaches a network DLP, the file is already ciphertext — nothing to inspect, nothing to block. Data Loss Prevention moves enforcement to the endpoint, before encryption.
Windows · Linux · macOS
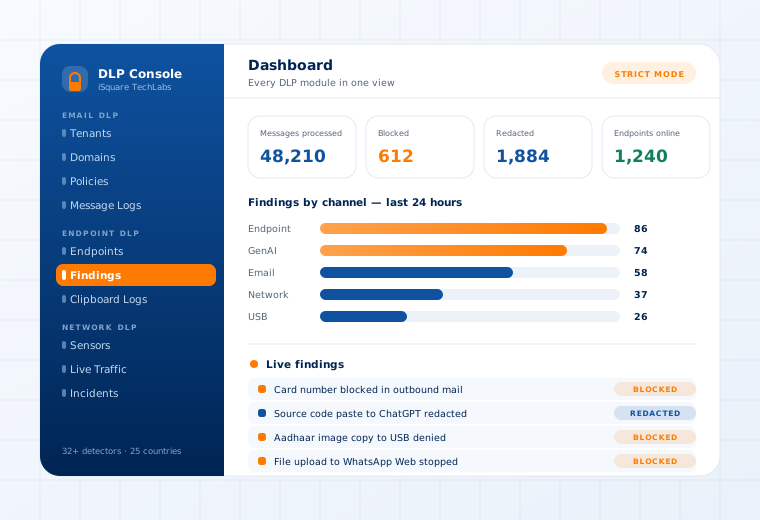
Write the rule once — enforce everywhere. All three modules read from a single pattern catalogue, and every finding lands in one console.
Runs on every device. Guards clipboard, USB, print, screenshot, file-save and image-open, with on-device OCR.
Inline email redact, quarantine or reject — plus a browser compose-window filter for Gmail, Outlook and Office 365.
Inspects encrypted web traffic on the device — blocks uploads to messaging, cloud and paste sites, and redacts AI prompts.
Prebuilt detectors for card numbers, national IDs and account data.
Random digit strings never raise a false alarm.
Regex editor with a test sandbox; changes propagate in seconds.
Built into the operating system, Data Loss Prevention stops sensitive data before an application can move it — which is why it cannot simply be bypassed.
A photo containing card or ID data is checked on the device before it opens — it never appears on screen if it is sensitive. Works in any viewer.
Saving a card or ID number to a file is blocked the instant you try — the data never reaches the disk.
Sensitive data is cleared the moment it is copied — no window in which to paste it somewhere it should not go.
Sensitive content closes the print dialog on every path — keyboard shortcut and File → Print alike.
Most DLP fails here — these apps encrypt the file on the device, so the network only sees scrambled data. We close the gap with three independent layers; all three must be beaten to leak a file.
Catches files in the browser — file picker, drag-drop or paste — before the web app can read them. Blocks 20+ high-risk sites.
Blocks uploads to messaging and file-sharing sites at the network layer — even when the file is encrypted.
Reads the chat window on screen to catch sensitive text typed or pasted into a message before it is sent.
20+ hosts including WhatsApp · Telegram · Signal · Messenger · Discord · Dropbox · MEGA · WeTransfer · Pastebin
Employees paste customer data into ChatGPT, Claude and Gemini every day. We inspect the prompt on the device — before it ever reaches the AI provider.
Sensitive text or images typed or pasted into ChatGPT, Claude, Gemini, Copilot and Perplexity are caught and blocked before the prompt is sent.
If the model echoes back a card or ID number, it is masked on screen — the user sees a redaction, never the secret itself.
Understands each AI's API shape, so prompts hidden inside streaming JSON bodies are still extracted and checked — not just plain text boxes.
Enforced in the browser and at the network layer on the endpoint, so it still works even though all AI traffic is HTTPS-encrypted.
*Card and ID numbers are checksum-validated, so random digit strings never raise a false alarm.
Maps out of the box to:
Tamper-proof audit log — evidence for every finding (file, user, time, action, masked match). Raw personal data never leaves your database.
Watch and log, block nothing. Prove ROI before a single user feels a block.
Silently redact or wipe. Sensitive content vanishes; workflows continue.
Hard-block with a user popup. Kernel-enforced denial with an on-screen notice.
Mode changes propagate via heartbeat in seconds — no agent re-install, no user logout.
Create departments — Finance, Executive, Engineering — colour-code them, and see member-device and policy counts at a glance.
Bind one detector profile to several departments at once. Edit the rule once and every group it covers updates live.
Move endpoints into a group from a single screen. A device's department decides which policy it enforces.
Groups bind by stable ID, so a rename never breaks enforcement — and the Default baseline cannot be deleted while in use.
Stops leaks through apps most DLP cannot reach.
Blocks at the OS layer — it cannot be bypassed.
Reads tilted, low-contrast camera shots.
Windows, Linux and macOS — one agent.
Rule and mode changes take effect in seconds.
Prove ROI before anyone feels a block.
Start in audit-only mode. The baseline scan alone usually surprises people — then you decide what to enforce.